Target New ArrivalsHalloweenChristmasGift IdeasClothing, Shoes & AccessoriesHome & DecorKitchen & DiningPatio, Lawn & GardenGroceryHousehold EssentialsBabyBeautyTarget Beauty StudioPersonal CareSports & OutdoorsPetsHealthWellnessSchool & Office SuppliesToys & GamesElectronics & TechVideo GamesBooks, Music & MoviesParty SuppliesGift CardsShop by CommunityTarget OpticalDealsClearanceNew ArrivalsBack to SchoolCollegeTop DealsTarget Circle DealsWeekly AdShop Order PickupShop Same Day DeliveryRegistryRedCardTarget CircleFind Stores
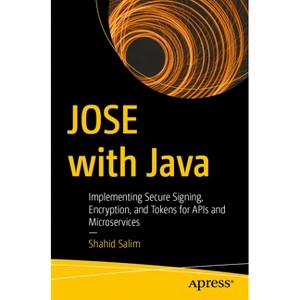
Jose with Java - by  Shahid Salim (Paperback) - 1 of 1

Jose with Java - by Shahid Salim (Paperback)

New at  target 
$54.99

Pre-order
Free & easy returns
Free & easy returns
Return this item by mail or in store within 90 days for a full refund.
Eligible for registries and wish lists

About this item

Highlights

  • Master secure signing, encryption and token handling in your Java applications with JOSE.
  • About the Author: Shahid Salim is a senior Java and security engineer with 25 years of extensive hands-on experience designing, implementing, and reviewing secure authentication and authorization systems using JWT, OAuth 2.0, and JOSE standards.
  • 190 Pages
  • Computers, Languages

Description


Book Synopsis


Master secure signing, encryption and token handling in your Java applications with JOSE. With this book, discover how to implement JWS, JWE, JWK, and JWT to build authentication and authorization systems that are scalable, interoperable and secure in real-world environments.

You'll explore JOSE from the ground up, beginning with core concepts such as cryptography, token structure, and validation logic. Through clear examples and step-by-step code, the book teaches you how to issue, parse, validate, encrypt, and decrypt tokens using Java's standard APIs and widely adopted JOSE libraries. You'll learn why vulnerabilities often stem not from broken cryptography but from incorrect validation, unsafe defaults, key mismanagement, and misunderstanding of claims. You'll learn to avoid common pitfalls and errors by designing and reviewing tokens with security correctness in mind.

This book bridges the gap between JOSE specifications and real Java implementations used in APIs, microservices, OAuth 2.0, and OpenID Connect systems. It draws on security audits, production failures, and enterprise requirements to show how JOSE breaks in practice and how to build defenses that last.

What You Will Learn:

    Correctly issue, parse, and validate JWTs in Java applications Choose between JWS and JWE based on concrete confidentiality and integrity needs Implement secure claim validation, including issuer, audience, expiration, and replay checks Manage cryptographic keys using JWKs, including rotation, lifecycle management, and safe storage Debug and analyze token failures in real production environments using structured techniques Identify and avoid common JOSE vulnerabilities, including algorithm confusion and unsafe defaults

Who This Book is for:

Backend Java developers, platform engineers and software architects working on APIs or distributed systems.


About the Author


Shahid Salim is a senior Java and security engineer with 25 years of extensive hands-on experience designing, implementing, and reviewing secure authentication and authorization systems using JWT, OAuth 2.0, and JOSE standards. He has worked on enterprise Java and microservice architectures where correct cryptographic usage, token validation, and key management are critical for security, compliance, and long-term maintainability.

Across multiple projects, he has encountered recurring JWT and JOSE vulnerabilities--such as algorithm confusion, incomplete claim validation, improper key rotation, and overreliance on framework defaults, even in experienced engineering teams. This book is shaped by those real-world failure modes and focuses on explaining not only how JOSE works, but why certain implementation choices are dangerous and how to avoid them.

He also brings an enterprise and regulatory perspective to the topic, including practical alignment with OAuth 2.0, OpenID Connect, and eIDAS requirements, which is rarely addressed in typical JWT-focused books.

Dimensions (Overall): 9.25 Inches (H) x 6.1 Inches (W)
Suggested Age: 22 Years and Up
Number of Pages: 190
Genre: Computers
Sub-Genre: Languages
Publisher: Apress
Theme: Java
Format: Paperback
Author: Shahid Salim
Language: English
Street Date: January 4, 2027
TCIN: 1014588567
UPC: 9798868830556
Item Number (DPCI): 247-65-3641
Origin: Made in the USA or Imported
If the item details aren’t accurate or complete, we want to know about it.

Shipping details

Estimated ship dimensions: 1 inches length x 6.1 inches width x 9.25 inches height
Estimated ship weight: 1 pounds
We regret that this item cannot be shipped to PO Boxes.
This item cannot be shipped to the following locations: American Samoa (see also separate entry under AS), Guam (see also separate entry under GU), Northern Mariana Islands, Puerto Rico (see also separate entry under PR), United States Minor Outlying Islands, Virgin Islands, U.S., APO/FPO, Alaska, Hawaii

Return details

This item can be returned to any Target store or Target.com.
This item must be returned within 90 days of the date it was purchased in store, delivered to the guest, delivered by a Shipt shopper, or picked up by the guest.
See the return policy for complete information.

Additional product information and recommendations

Discover more options

Skip to next section

Best-selling Computers & Technology Books

Skip to next section

Get top deals, latest trends, and more.